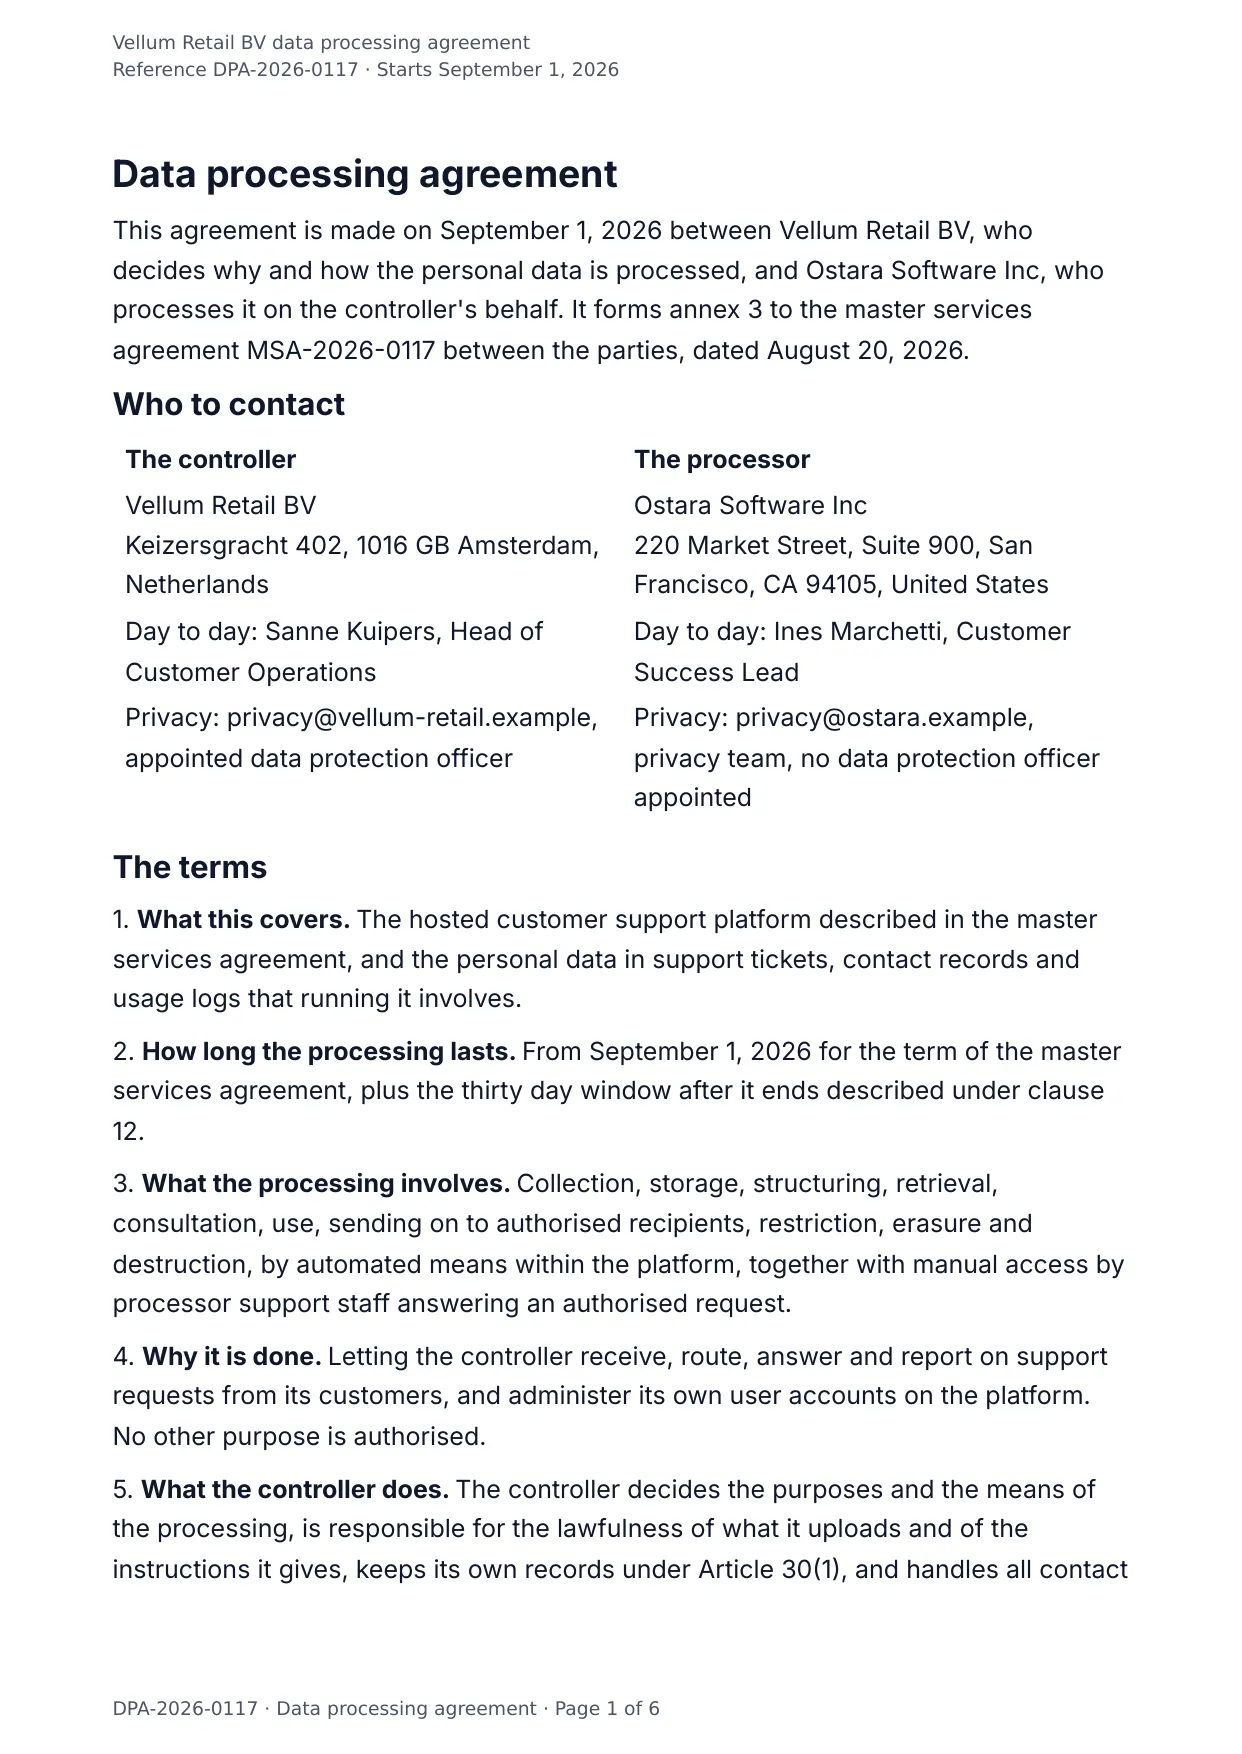
The first page of the document DocMake makes from the sample values on this page.
Legal
Data Processing Agreement
A data processing agreement is the contract a controller puts in place with a processor before that processor touches personal data on its behalf. The GDPR requires the contract to exist and to be in writing, including in electronic form. It does not prescribe a template, which is why every vendor agreement you receive looks different while covering broadly the same ground.
Article 28(3) sets the content in two layers. The framing first: the subject matter and duration of the processing, its nature and purpose, the type of personal data and the categories of data subject, and the obligations and rights of the controller. Then eight lettered processor obligations, from processing only on documented instructions including as to international transfers, through confidentiality commitments, the security measures of Article 32, the conditions for engaging another processor, assistance with data subject rights, assistance with Articles 32 to 36, deletion or return of the data at the controller's choice when the service ends, and making available the information needed to demonstrate compliance while allowing for and contributing to audits and inspections. The processor also has to tell the controller immediately if an instruction appears to it to infringe the regulation.
Three related duties sit alongside those clauses rather than inside them. Sub-processors need prior specific or general written authorisation, the same obligations flow down by contract, and the first processor stays fully liable for the second. Article 30(2) puts a separate record keeping duty on the processor. Article 33(2) obliges the processor to notify the controller without undue delay after becoming aware of a personal data breach, which is a different thing from the controller's own seventy two hour clock to the supervisory authority. The Commission adopted standard contractual clauses for controller to processor contracts in June 2021, a distinct instrument from the international transfer clauses adopted the same day, with annexes for the parties, the description of the processing, the technical and organisational measures and the sub-processors.
This page describes what such an agreement customarily contains. It is not legal advice, and nothing produced from a template is compliant by virtue of having been generated. European guidance is blunt about the usual failure: an agreement that merely restates the regulation is not enough, and the specifics of how each requirement will be met and what level of security applies are the reason the contract is negotiated at all. Let your own counsel and your data protection officer settle the substance. Where generation earns its place is the mechanical half: the annexes differ per customer, the sub-processor list changes every quarter, and having every executed copy descend from one record beats maintaining forty near identical files that quietly drift apart.
Blanks to fill
| effective_date | Date it starts |
| controller_name | Controller |
| processor_name | Processor |
| main_agreement | The agreement it forms part of |
| controller_address | Where the controller is |
| processor_address | Where the processor is |
| controller_contact | Controller contact |
| processor_contact | Processor contact |
| controller_privacy_contact | Controller privacy contact |
| processor_privacy_contact | Processor privacy contact |
| subject_matter | What is being processed |
| duration | How long the processing lasts |
| nature_of_processing | What the processing involves |
| purpose_of_processing | Why the processing is done |
| controller_duties | What the controller does |
| documented_instructions | The instructions the processor follows |
| subprocessor_authorisation | How other processors are authorised |
| objection_period | Time to object |
| breach_notification | Telling the controller about a breach |
| assistance | How the processor helps the controller |
| audits | Information and audits |
| deletion_or_return | What happens to the data at the end |
| records_kept | The records the processor keeps |
| international_transfers | Data that leaves the European Economic Area |
| signed_date | Date it was signed |
| controller_signatory | Who signs for the controller |
| controller_signatory_role | Their role |
| processor_signatory | Who signs for the processor |
| processor_signatory_role | Their role |
| agreement_reference | Agreement reference |
| processor_obligations[] | One per item, so a row is added for every item in the list |
| data_categories[] | One per item, so a row is added for every item in the list |
| data_subjects[] | One per item, so a row is added for every item in the list |
| security_measures[] | One per item, so a row is added for every item in the list |
| subprocessors[] | One per item, so a row is added for every item in the list |
The data behind the preview
This is the exact JSON that produced the document above. Change the values, POST them to the API, and you get your version back as DOCX or PDF. Lists grow and shrink with your data; the layout adapts.
- 01 Sign up free and duplicate this template into your workspace.
- 02 Adjust the wording and branding in the visual editor.
- 03 Fill it in the app, share it as a form link, or call the API.
{
  "agreement_reference": "DPA-2026-0117",
  "effective_date": "September 1, 2026",
  "main_agreement": "It forms annex 3 to the master services agreement MSA-2026-0117 between the parties, dated August 20, 2026.",
  "controller_name": "Vellum Retail BV",
  "controller_address": "Keizersgracht 402, 1016 GB Amsterdam, Netherlands",
  "controller_contact": "Sanne Kuipers, Head of Customer Operations",
  "controller_privacy_contact": "privacy@vellum-retail.example, appointed data protection officer",
  "processor_name": "Ostara Software Inc",
  "processor_address": "220 Market Street, Suite 900, San Francisco, CA 94105, United States",
  "processor_contact": "Ines Marchetti, Customer Success Lead",
  "processor_privacy_contact": "privacy@ostara.example, privacy team, no data protection officer appointed",
  "subject_matter": "The hosted customer support platform described in the master services agreement, and the personal data in support tickets, contact records and usage logs that running it involves.",
  "duration": "From September 1, 2026 for the term of the master services agreement, plus the thirty day window after it ends described under clause 12.",
  "nature_of_processing": "Collection, storage, structuring, retrieval, consultation, use, sending on to authorised recipients, restriction, erasure and destruction, by automated means within the platform, together with manual access by processor support staff answering an authorised request.",
  "purpose_of_processing": "Letting the controller receive, route, answer and report on support requests from its customers, and administer its own user accounts on the platform. No other purpose is authorised.",
  "controller_duties": "The controller decides the purposes and the means of the processing, is responsible for the lawfulness of what it uploads and of the instructions it gives, keeps its own records under Article 30(1), and handles all contact with data subjects and with its supervisory authority.",
  "documented_instructions": "The master services agreement, this agreement and its annexes, the settings the controller chooses in the platform, and any further instruction given in writing through the named contacts. The processor tells the controller before processing otherwise where the law requires it to, unless that law forbids the notice.",
  "processor_obligations": [
    {
      "article": "28(3)(a)",
      "obligation": "Process the personal data only on the controller's documented instructions, transfers to other countries included",
      "how_it_is_met": "Instructions are limited to those above. Support staff act on ticket based requests only, and the processor tells the controller at once if an instruction looks unlawful to it."
    },
    {
      "article": "28(3)(b)",
      "obligation": "Make sure the people allowed to process the data have promised to keep it confidential",
      "how_it_is_met": "Every employee and contractor signs a confidentiality undertaking on joining, renewed each year, and finishes data protection training before any live access is granted."
    },
    {
      "article": "28(3)(c)",
      "obligation": "Take the measures required by Article 32",
      "how_it_is_met": "The measures in annex 2, reviewed at least once a year and after any material change to the service."
    },
    {
      "article": "28(3)(d)",
      "obligation": "Respect the conditions for bringing in another processor",
      "how_it_is_met": "General written authorisation as described in clause 8, the same duties imposed on each of them by contract, and the processor answerable for their work."
    },
    {
      "article": "28(3)(e)",
      "obligation": "Help the controller answer requests from people exercising their rights",
      "how_it_is_met": "Search, export, correction, restriction and deletion tools are in the platform for controller administrators. Where a request cannot be served through them, the processor answers in writing within five working days."
    },
    {
      "article": "28(3)(f)",
      "obligation": "Help the controller meet Articles 32 to 36",
      "how_it_is_met": "Security documentation, breach information, an impact assessment pack for the service, and support for any prior consultation the controller has to make."
    },
    {
      "article": "28(3)(g)",
      "obligation": "Delete or return the personal data at the end of the service, and delete the copies",
      "how_it_is_met": "The controller chooses deletion or export in writing before the end. Where no choice is made, clause 12 applies."
    },
    {
      "article": "28(3)(h)",
      "obligation": "Make available what is needed to show compliance, and allow audits",
      "how_it_is_met": "The yearly audit report and penetration test summary on request, plus one audit led by the controller each year on thirty days notice, or sooner after a breach affecting its data."
    }
  ],
  "subprocessor_authorisation": "General written authorisation. The processor keeps the list in annex 3 current and gives the controller written notice at least thirty days before adding or replacing any of them.",
  "objection_period": "thirty days of that notice, and where the parties cannot agree an alternative the controller may end the affected service without penalty.",
  "breach_notification": "The processor tells the controller without undue delay after learning of a personal data breach affecting the controller's data, and within twenty four hours in any event, with what is known at the time and more as the investigation goes on. It does not notify the supervisory authority or the people affected on the controller's behalf unless separately instructed in writing.",
  "assistance": "Help under Article 28(3)(e) and (f) costs nothing for requests arising from ordinary use of the service. Work beyond that, such as forensic work asked for by the controller past the processor's own investigation, is quoted in advance.",
  "audits": "The processor provides its yearly independent audit report, its penetration test summary and a completed security questionnaire. Where those do not answer the question, the controller or an auditor it appoints may audit once a year on thirty days written notice, in business hours, without access to any other customer's data, and under confidentiality.",
  "deletion_or_return": "Within thirty days of the end, the controller may ask for an export in a structured, commonly used, machine readable form, or for deletion. Where no instruction arrives in that time, the processor deletes the personal data and the copies of it, apart from backups that expire on the thirty five day cycle, and confirms the deletion in writing.",
  "records_kept": "The processor keeps records of the kinds of processing it carries out for the controller under Article 30(2), including transfers to other countries and a general description of the security measures, and makes them available to the controller or a supervisory authority on request.",
  "data_categories": [
    {
      "kind_of_data": "Contact and identity",
      "what_it_covers": "Name, email address, telephone number, postal address, customer reference, preferred language",
      "special_category": "No"
    },
    {
      "kind_of_data": "Support conversations",
      "what_it_covers": "Ticket subject and body, attachments the requester uploads, chat transcripts, call notes, satisfaction ratings",
      "special_category": "No, though free text may hold whatever the requester chooses to write"
    },
    {
      "kind_of_data": "Orders and accounts",
      "what_it_covers": "Order number, order date, order value, delivery status, returns and refunds, loyalty tier",
      "special_category": "No"
    },
    {
      "kind_of_data": "Platform use and technical",
      "what_it_covers": "User account identifier, role, address of the device, browser string, session times, audit log entries",
      "special_category": "No"
    }
  ],
  "data_subjects": [
    {
      "group_of_people": "Customers of the controller",
      "description": "People in the Netherlands, Belgium and Germany who contact the controller's support team about an order or an account"
    },
    {
      "group_of_people": "Staff and contractors of the controller",
      "description": "Agents, team leads and administrators holding accounts on the platform"
    },
    {
      "group_of_people": "Third party contacts",
      "description": "Delivery partner staff and shop staff named in a ticket where a request involves them"
    }
  ],
  "security_measures": [
    {
      "area": "Encryption",
      "measure": "Data encrypted in transit with TLS 1.3 and at rest with AES 256. Analytics exports are stripped of identifiers before they leave the live boundary."
    },
    {
      "area": "Access control",
      "measure": "Access by role, named accounts only, two factors required, access reviewed every quarter, live access granted only when needed and always logged."
    },
    {
      "area": "Keeping data whole",
      "measure": "Live and test environments are separate, no live personal data reaches a test system, and every change is peer reviewed and tested before release."
    },
    {
      "area": "Staying available",
      "measure": "Deployed across three zones, encrypted backups every six hours kept for thirty five days, restores tested quarterly, recovery targets written into annex 2."
    },
    {
      "area": "Testing",
      "measure": "An independent penetration test each year, continuous dependency scanning, and a review of these measures yearly and after any material change."
    },
    {
      "area": "Physical security",
      "measure": "Data centres run by the hosting provider under its own certified regime, with certificates available on request."
    },
    {
      "area": "People",
      "measure": "Screening where the law allows, confidentiality undertakings, yearly training, and a documented process for joiners and leavers."
    }
  ],
  "subprocessors": [
    {
      "name": "Cloud hosting provider",
      "service": "Hosting, live and backup storage of the database",
      "location": "Netherlands and Germany",
      "transfer_basis": "Stays in the European Economic Area",
      "added": "September 1, 2026"
    },
    {
      "name": "Email provider",
      "service": "Sending ticket notices and survey email",
      "location": "Ireland, support from the USA",
      "transfer_basis": "Standard contractual clauses, module three",
      "added": "September 1, 2026"
    },
    {
      "name": "Error monitoring service",
      "service": "Catching and alerting on application errors",
      "location": "United States",
      "transfer_basis": "Standard contractual clauses, plus scrubbing first",
      "added": "September 1, 2026"
    },
    {
      "name": "Out of hours support partner",
      "service": "First line cover between 22:00 and 06:00",
      "location": "Portugal",
      "transfer_basis": "Stays in the European Economic Area",
      "added": "February 3, 2027"
    }
  ],
  "international_transfers": "The personal data is stored in the European Economic Area. Access from the United States by the processor's support staff, and the transfers to the other processors named in annex 3, take place under the standard contractual clauses for transfers to other countries, together with the extra measures recorded in annex 2.",
  "signed_date": "August 28, 2026",
  "controller_signatory": "Sanne Kuipers",
  "controller_signatory_role": "Head of Customer Operations, Vellum Retail BV",
  "processor_signatory": "Ines Marchetti",
  "processor_signatory_role": "Vice President, Customer Success, Ostara Software Inc"
}
Generate this document via the API
One template plus changing data is the whole point. The list of blanks above is the contract, and every new set of values comes back in the same layout: fill it in the app, hand someone a form link, or POST the JSON and get the file straight back.
The request below carries this page's own values, so it runs as soon as the template exists in your workspace. Swap the values for yours and the response is your document.
curl -X POST https://app.docmake.io/api/v1/render \
  -H "Authorization: Bearer $DOCMAKE_API_KEY" \
  -H "Content-Type: application/json" \
  -H "Accept: application/json" \
  --output data-processing-agreement.pdf \
  --data-binary @- <<'JSON'
{
  "template_id": "tmpl_your_template_id",
  "format": "pdf",
  "data": {
    "agreement_reference": "DPA-2026-0117",
    "effective_date": "September 1, 2026",
    "main_agreement": "It forms annex 3 to the master services agreement MSA-2026-0117 between the parties, dated August 20, 2026.",
    "controller_name": "Vellum Retail BV",
    "controller_address": "Keizersgracht 402, 1016 GB Amsterdam, Netherlands",
    "controller_contact": "Sanne Kuipers, Head of Customer Operations",
    "controller_privacy_contact": "privacy@vellum-retail.example, appointed data protection officer",
    "processor_name": "Ostara Software Inc",
    "processor_address": "220 Market Street, Suite 900, San Francisco, CA 94105, United States",
    "processor_contact": "Ines Marchetti, Customer Success Lead",
    "processor_privacy_contact": "privacy@ostara.example, privacy team, no data protection officer appointed",
    "subject_matter": "The hosted customer support platform described in the master services agreement, and the personal data in support tickets, contact records and usage logs that running it involves.",
    "duration": "From September 1, 2026 for the term of the master services agreement, plus the thirty day window after it ends described under clause 12.",
    "nature_of_processing": "Collection, storage, structuring, retrieval, consultation, use, sending on to authorised recipients, restriction, erasure and destruction, by automated means within the platform, together with manual access by processor support staff answering an authorised request.",
    "purpose_of_processing": "Letting the controller receive, route, answer and report on support requests from its customers, and administer its own user accounts on the platform. No other purpose is authorised.",
    "controller_duties": "The controller decides the purposes and the means of the processing, is responsible for the lawfulness of what it uploads and of the instructions it gives, keeps its own records under Article 30(1), and handles all contact with data subjects and with its supervisory authority.",
    "documented_instructions": "The master services agreement, this agreement and its annexes, the settings the controller chooses in the platform, and any further instruction given in writing through the named contacts. The processor tells the controller before processing otherwise where the law requires it to, unless that law forbids the notice.",
    "processor_obligations": [
      {
        "article": "28(3)(a)",
        "obligation": "Process the personal data only on the controller's documented instructions, transfers to other countries included",
        "how_it_is_met": "Instructions are limited to those above. Support staff act on ticket based requests only, and the processor tells the controller at once if an instruction looks unlawful to it."
      },
      {
        "article": "28(3)(b)",
        "obligation": "Make sure the people allowed to process the data have promised to keep it confidential",
        "how_it_is_met": "Every employee and contractor signs a confidentiality undertaking on joining, renewed each year, and finishes data protection training before any live access is granted."
      },
      {
        "article": "28(3)(c)",
        "obligation": "Take the measures required by Article 32",
        "how_it_is_met": "The measures in annex 2, reviewed at least once a year and after any material change to the service."
      },
      {
        "article": "28(3)(d)",
        "obligation": "Respect the conditions for bringing in another processor",
        "how_it_is_met": "General written authorisation as described in clause 8, the same duties imposed on each of them by contract, and the processor answerable for their work."
      },
      {
        "article": "28(3)(e)",
        "obligation": "Help the controller answer requests from people exercising their rights",
        "how_it_is_met": "Search, export, correction, restriction and deletion tools are in the platform for controller administrators. Where a request cannot be served through them, the processor answers in writing within five working days."
      },
      {
        "article": "28(3)(f)",
        "obligation": "Help the controller meet Articles 32 to 36",
        "how_it_is_met": "Security documentation, breach information, an impact assessment pack for the service, and support for any prior consultation the controller has to make."
      },
      {
        "article": "28(3)(g)",
        "obligation": "Delete or return the personal data at the end of the service, and delete the copies",
        "how_it_is_met": "The controller chooses deletion or export in writing before the end. Where no choice is made, clause 12 applies."
      },
      {
        "article": "28(3)(h)",
        "obligation": "Make available what is needed to show compliance, and allow audits",
        "how_it_is_met": "The yearly audit report and penetration test summary on request, plus one audit led by the controller each year on thirty days notice, or sooner after a breach affecting its data."
      }
    ],
    "subprocessor_authorisation": "General written authorisation. The processor keeps the list in annex 3 current and gives the controller written notice at least thirty days before adding or replacing any of them.",
    "objection_period": "thirty days of that notice, and where the parties cannot agree an alternative the controller may end the affected service without penalty.",
    "breach_notification": "The processor tells the controller without undue delay after learning of a personal data breach affecting the controller's data, and within twenty four hours in any event, with what is known at the time and more as the investigation goes on. It does not notify the supervisory authority or the people affected on the controller's behalf unless separately instructed in writing.",
    "assistance": "Help under Article 28(3)(e) and (f) costs nothing for requests arising from ordinary use of the service. Work beyond that, such as forensic work asked for by the controller past the processor's own investigation, is quoted in advance.",
    "audits": "The processor provides its yearly independent audit report, its penetration test summary and a completed security questionnaire. Where those do not answer the question, the controller or an auditor it appoints may audit once a year on thirty days written notice, in business hours, without access to any other customer's data, and under confidentiality.",
    "deletion_or_return": "Within thirty days of the end, the controller may ask for an export in a structured, commonly used, machine readable form, or for deletion. Where no instruction arrives in that time, the processor deletes the personal data and the copies of it, apart from backups that expire on the thirty five day cycle, and confirms the deletion in writing.",
    "records_kept": "The processor keeps records of the kinds of processing it carries out for the controller under Article 30(2), including transfers to other countries and a general description of the security measures, and makes them available to the controller or a supervisory authority on request.",
    "data_categories": [
      {
        "kind_of_data": "Contact and identity",
        "what_it_covers": "Name, email address, telephone number, postal address, customer reference, preferred language",
        "special_category": "No"
      },
      {
        "kind_of_data": "Support conversations",
        "what_it_covers": "Ticket subject and body, attachments the requester uploads, chat transcripts, call notes, satisfaction ratings",
        "special_category": "No, though free text may hold whatever the requester chooses to write"
      },
      {
        "kind_of_data": "Orders and accounts",
        "what_it_covers": "Order number, order date, order value, delivery status, returns and refunds, loyalty tier",
        "special_category": "No"
      },
      {
        "kind_of_data": "Platform use and technical",
        "what_it_covers": "User account identifier, role, address of the device, browser string, session times, audit log entries",
        "special_category": "No"
      }
    ],
    "data_subjects": [
      {
        "group_of_people": "Customers of the controller",
        "description": "People in the Netherlands, Belgium and Germany who contact the controller's support team about an order or an account"
      },
      {
        "group_of_people": "Staff and contractors of the controller",
        "description": "Agents, team leads and administrators holding accounts on the platform"
      },
      {
        "group_of_people": "Third party contacts",
        "description": "Delivery partner staff and shop staff named in a ticket where a request involves them"
      }
    ],
    "security_measures": [
      {
        "area": "Encryption",
        "measure": "Data encrypted in transit with TLS 1.3 and at rest with AES 256. Analytics exports are stripped of identifiers before they leave the live boundary."
      },
      {
        "area": "Access control",
        "measure": "Access by role, named accounts only, two factors required, access reviewed every quarter, live access granted only when needed and always logged."
      },
      {
        "area": "Keeping data whole",
        "measure": "Live and test environments are separate, no live personal data reaches a test system, and every change is peer reviewed and tested before release."
      },
      {
        "area": "Staying available",
        "measure": "Deployed across three zones, encrypted backups every six hours kept for thirty five days, restores tested quarterly, recovery targets written into annex 2."
      },
      {
        "area": "Testing",
        "measure": "An independent penetration test each year, continuous dependency scanning, and a review of these measures yearly and after any material change."
      },
      {
        "area": "Physical security",
        "measure": "Data centres run by the hosting provider under its own certified regime, with certificates available on request."
      },
      {
        "area": "People",
        "measure": "Screening where the law allows, confidentiality undertakings, yearly training, and a documented process for joiners and leavers."
      }
    ],
    "subprocessors": [
      {
        "name": "Cloud hosting provider",
        "service": "Hosting, live and backup storage of the database",
        "location": "Netherlands and Germany",
        "transfer_basis": "Stays in the European Economic Area",
        "added": "September 1, 2026"
      },
      {
        "name": "Email provider",
        "service": "Sending ticket notices and survey email",
        "location": "Ireland, support from the USA",
        "transfer_basis": "Standard contractual clauses, module three",
        "added": "September 1, 2026"
      },
      {
        "name": "Error monitoring service",
        "service": "Catching and alerting on application errors",
        "location": "United States",
        "transfer_basis": "Standard contractual clauses, plus scrubbing first",
        "added": "September 1, 2026"
      },
      {
        "name": "Out of hours support partner",
        "service": "First line cover between 22:00 and 06:00",
        "location": "Portugal",
        "transfer_basis": "Stays in the European Economic Area",
        "added": "February 3, 2027"
      }
    ],
    "international_transfers": "The personal data is stored in the European Economic Area. Access from the United States by the processor's support staff, and the transfers to the other processors named in annex 3, take place under the standard contractual clauses for transfers to other countries, together with the extra measures recorded in annex 2.",
    "signed_date": "August 28, 2026",
    "controller_signatory": "Sanne Kuipers",
    "controller_signatory_role": "Head of Customer Operations, Vellum Retail BV",
    "processor_signatory": "Ines Marchetti",
    "processor_signatory_role": "Vice President, Customer Success, Ostara Software Inc"
  }
}
JSON
tmpl_your_template_id is
a stand-in: build this template in the visual editor and copy the id it shows, or create one with POST /api/v1/templates. Keys, formats, strict mode and batches are in the API reference.
Or let an AI assistant do it
The DocMake MCP server lets Claude and other assistants make this document the same way. Install it once:
claude mcp add docmake \
  --env DOCMAKE_API_KEY=dm_your_api_key \
  -- npx -y @docmake/mcp@latest
Then ask for the document in plain words:
Make a PDF from my Data Processing Agreement template with date it starts "September 1, 2026" and controller "Vellum Retail BV".
More legal templates
Bill of Sale
A record of goods sold from one party to another, with a table of the items, the price paid, and the day they are collected.
View template →Commercial Lease Agreement
A lease for business premises with the rent, the deposit, who looks after what, and the fixtures recorded at handover.
View template →Employment Contract
A contract for a new hire with the role, the pay, the hours, the time off, and the notice each side has to give.
View template →